Dating Platform Payment Risk & Chargeback Prevention Guide
Analyze root causes of payment fraud and friendly chargebacks in dating apps—and implement controls across velocity rules, 3DS2, descriptors, and support.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Author
Cropay Payment Architecture Editorial Team
Fact & Compliance Review
Cropay Business & Compliance Review Group
Last Fact Review
Dating platforms face unique dispute patterns: users may forget a purchase, fail to recognize a corporate billing descriptor, or file a chargeback when they cannot easily find a refund button. Reducing disputes requires coordinated product, risk, and customer support design.
Key Risk Scenarios & Countermeasures
Stolen Cards & Velocity Attacks
Enforce per-user and per-card daily attempt limits, IP/country consistency checks, and mandatory 3DS2 on suspicious orders.
Unrecognized Billing Descriptors
Display the exact statement descriptor on the checkout page and in email receipts so cardholders recognize the charge.
Expectation Mismatch & Buyer Remorse
Ensure marketing copy and unlock prompts accurately describe what the user receives, avoiding exaggerated claims.
Inaccessible Support Escalations
Place a visible billing support entry inside the user profile so billing questions are resolved via refunds rather than bank disputes.
Four-Stage Dispute Prevention & Response Loop
01 Pre-Purchase Disclosure
Present clear pricing, one-time payment terms, and refund rules prior to payment initiation.
02 Authentication & Velocity Gate
Screen abnormal card binding or high-frequency attempts and trigger 3D Secure 2 verification.
03 Post-Purchase Receipt & Support
Send an immediate confirmation receipt showing order ID, amount, descriptor, and support contact.
04 Evidence Packaging for Disputes
Export login logs, 3DS2 records, and feature usage timestamps when contesting invalid chargebacks.
Capabilities, Evidence & Compliance Boundaries
Product Governance Comes First
Gateway risk rules cannot compensate for deceptive product flows or fake user engagement practices.
Proactive Refunds Beat Chargebacks
Issuing a timely refund for a dissatisfied user is far more cost-effective than incurring a formal card network chargeback.
Ongoing Threshold Monitoring
Track dispute rates by traffic source, country, and price tier to adjust 3DS2 and velocity thresholds early.
References & scope
References & Applicable Scope
Applicable Regions: Reviewed per merchant target markets and current regulatory policies
- Cropay Business Fact Baseline & Security Compliance Documentation (Verified on 2026-08-27)
Risk & 3DS2 architecture
Four-Stage Fraud Screening, 3DS2 & Chargeback Defense Architecture
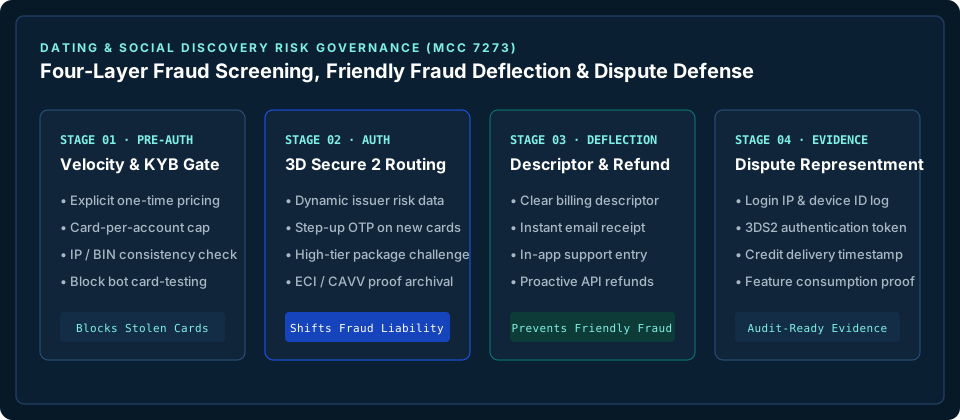
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Why do cardholders file "unrecognized transaction" disputes even after using the app?
Often the legal corporate name on their bank statement differs from the app brand name, or family members share a card without realizing it.
How many different cards should a single dating account be allowed to try?
We recommend strict limits on distinct cards per account and per device within 24 hours to prevent card testing.
What usage logs are most helpful in representment?
Timestamps showing the user logged in, completed 3DS2, received the credits, and actively sent messages or used features afterward.
Business assessment
Review Your Dating Platform’s Risk & Dispute Strategy
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment