Industry Payment Integration, Risk & Compliance Guides
Actionable guides for product, engineering, and risk teams building cross-border payment flows for dating, social discovery, and live streaming platforms.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Our guides focus on real operational decisions—how to prepare a dating or live streaming platform for acquiring underwriting, how to design one-time checkout and webhook state machines, and how to control fraud and chargebacks.
Guide Categories
Dating Platform Payment Guides
Cover merchant underwriting preparation, one-time checkout design, descriptor clarity, and friendly fraud prevention.
Live Streaming & Content Guides
Detail virtual coin top-up architecture, live gifting records, pay-per-view unlocks, and velocity controls.
App & Web Compliance Checklists
Prepare user terms, refund disclosures, support channels, and payment flow alignment across web and mobile apps.
3D Secure 2 & Risk Implementation
Understand frictionless vs. challenge 3DS2 flows, webhook synchronization, and dispute evidence logging.
Recommended Reading Path by Role
01 Business & Operations Teams
Start with the App & Web Compliance Guide and industry solution pages to prepare onboarding disclosures.
02 Product & Checkout Designers
Review the Dating or Live Streaming Integration Guides to structure order confirmation and refund flows.
03 Risk & Support Teams
Study the Dating Payment Risk Guide and 3D Secure 2 Guide to align velocity rules and dispute evidence.
04 Engineering Teams
Combine the integration guides with the Payment Gateway page to implement idempotent webhooks and error handling.
Capabilities, Evidence & Compliance Boundaries
Operational Reference Only
Guides provide practical architecture patterns; actual channel rules and parameters depend on your approved merchant setup.
One-Time Payment Scope
All examples and workflows focus on user-initiated one-time transactions, excluding automated subscription billing.
Regular Fact Review
Guides are reviewed against Cropay’s internal compliance baseline and updated as channel policies evolve.
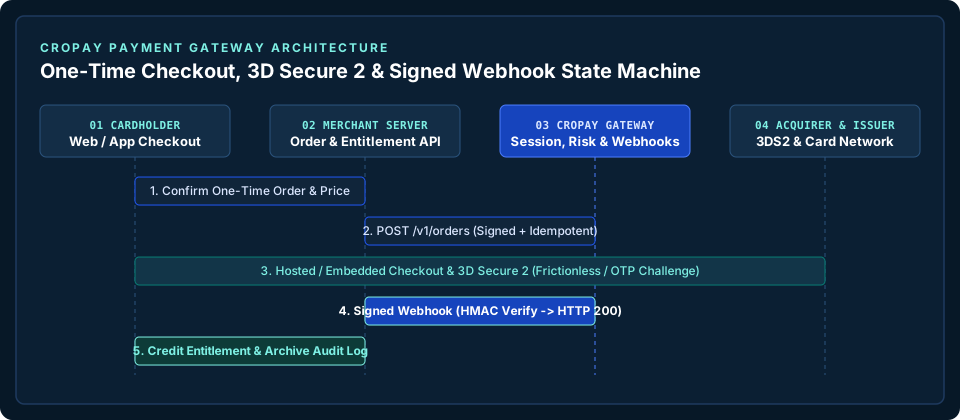
Gateway sequence diagram
One-Time Checkout, 3DS2 & Signed Webhook Sequence Architecture
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Which guide should we read first before applying for a merchant account?
Start with the App & Web Payment Compliance Guide and the integration guide for your specific vertical (Dating or Live Streaming).
Do these guides contain live production API endpoints?
They explain architectural workflows and state machines; live API endpoints and credentials are provided after business pre-review.
Why do the guides emphasize one-time payments over subscriptions?
Because Cropay’s verified scope currently covers one-time user-initiated transactions only, avoiding unverified recurring billing claims.
Business assessment
Discuss Your Platform’s Payment Architecture with Cropay
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment