Payment Fraud Prevention, 3DS2 & Chargeback Management
Connect pre-authorization velocity checks, 3DS2 authentication, clear descriptors, refund deflection, and dispute evidence across the payment lifecycle.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
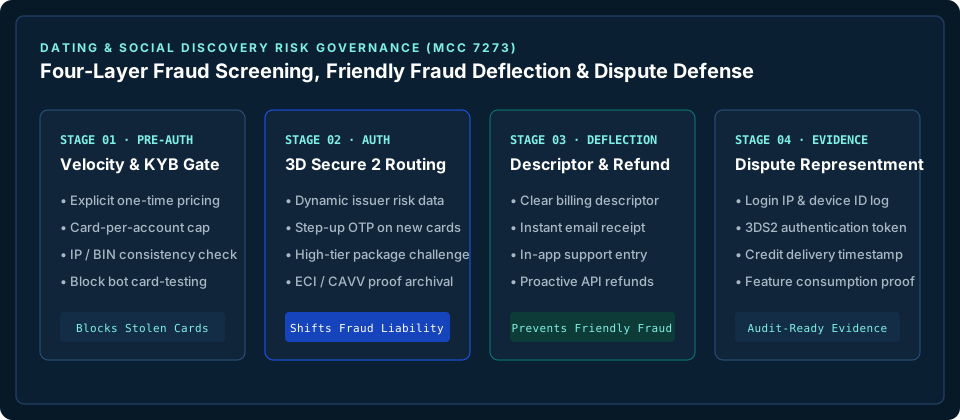
In dating and live streaming platforms, chargebacks stem from two primary sources: unauthorized card use (stolen cards or card testing) and friendly fraud (unrecognized descriptors, impulse buyer remorse, or unresolved support requests). Effective risk control addresses both.
Four Layers of Fraud & Chargeback Control
Pre-Authorization Velocity & Screening
Block automated card testing, abnormal IP/card velocity, and mismatched account parameters before authorization.
3D Secure 2 Authentication
Enforce cardholder identity verification on high-risk or high-value orders to reduce unauthorized fraud.
Friendly Fraud Deflection
Prevent disputes before they happen through transparent checkout disclosures, clear descriptors, and responsive refunds.
Structured Dispute Evidence
Compile 3DS2 proof, user login logs, IP/device records, and digital delivery timestamps when responding to disputes.
End-to-End Risk & Dispute Workflow
01 Pre-Checkout Risk Check
Validate account age, purchase frequency, card binding limits, and order amount thresholds.
02 3DS2 Authentication & Capture
Route transactions through 3DS2 verification according to channel rules and risk signals.
03 Customer Support & Refund Resolution
Resolve legitimate refund or cancellation requests promptly to avoid cardholder escalation to issuing banks.
04 Chargeback Alert & Representment
Review dispute reason codes and submit verifiable fulfillment and authentication evidence within network deadlines.
Capabilities, Evidence & Compliance Boundaries
No "Zero Chargeback" Guarantees
Cardholders always retain the right to initiate disputes through their issuing banks; no payment provider can guarantee 100% immunity or win rates.
3DS2 Does Not Cover Service Disputes
While 3DS2 helps address unauthorized fraud claims, it does not prevent disputes over product quality, unfulfilled services, or misleading terms.
Merchant Compliance Responsibility
Merchants must maintain dispute ratios within card scheme thresholds; excessive chargebacks may trigger channel limits or termination.
Risk & 3DS2 architecture
Four-Stage Fraud Screening, 3DS2 & Chargeback Defense Architecture
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
What is the difference between a refund and a chargeback?
A refund is resolved directly between the merchant and the user via the payment gateway; a chargeback is a formal dispute initiated by the cardholder’s issuing bank.
Does enabling 3D Secure 2 eliminate all chargebacks?
No. 3DS2 significantly reduces unauthorized transaction disputes, but cardholders can still file disputes for service non-delivery or billing misunderstandings.
What records should our platform log to support dispute representment?
Log user registration timestamps, login IP and device IDs, explicit checkout confirmation, 3DS2 results, and timestamps of digital credit delivery or consumption.
Business assessment
Evaluate Your Platform’s Fraud & Chargeback Controls
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment