Dating Platform Payment Integration Guide: From Underwriting to Go-Live
Practical guide for dating and social platforms covering pre-onboarding readiness, one-time checkout design, 3DS2 redirects, webhooks, and refund sync.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Author
Cropay Payment Architecture Editorial Team
Fact & Compliance Review
Cropay Business & Compliance Review Group
Last Fact Review
Successful payment integration for a dating platform starts before writing API code. Aligning your pricing disclosures, user confirmation steps, webhook state machines, and customer support entry points ensures smoother underwriting and higher checkout reliability.
Four Core Integration Modules for Dating Platforms
Pre-Underwriting Product Readiness
Ensure registration, age verification, transparent pricing, terms of use, privacy policy, and refund rules are live and accessible.
Transparent One-Time Checkout
Clearly display item name, quantity, currency, and one-time charge nature before initiating a payment session.
Idempotent Webhook Fulfillment
Grant credits or unlock features strictly upon verifying signed server webhooks rather than client browser redirects.
Closed-Loop Refund Synchronization
Deduct unspent credits or adjust entitlements automatically when a refund or dispute notification is received.
Step-by-Step Integration Workflow
01 Business & Website Pre-Check
Complete the compliance checklist for product pages, billing descriptors, and customer support channels.
02 Order Session & 3DS2 Setup
Integrate server-side order creation and handle 3DS2 redirect and return flows gracefully.
03 Webhook & Query Fallback
Implement signature verification, idempotent order updates, and active status polling for pending orders.
04 Sandbox End-to-End Acceptance
Test successful payments, 3DS2 failures, timeouts, and refunds in sandbox before production cutover.
Capabilities, Evidence & Compliance Boundaries
No Auto-Renewal Flows
Checkout copy and backend logic must not trigger automated recurring charges; every purchase requires active user confirmation.
Strict Domain Whitelisting
Production transactions may only originate from domains and apps reviewed and approved during underwriting.
Fulfillment Audit Trail
Retain complete order, IP, device, and entitlement delivery logs to support post-payment customer inquiries.
References & scope
References & Applicable Scope
Applicable Regions: Reviewed per merchant target markets and current regulatory policies
- Cropay Business Fact Baseline & Security Compliance Documentation (Verified on 2026-08-27)
Risk & 3DS2 architecture
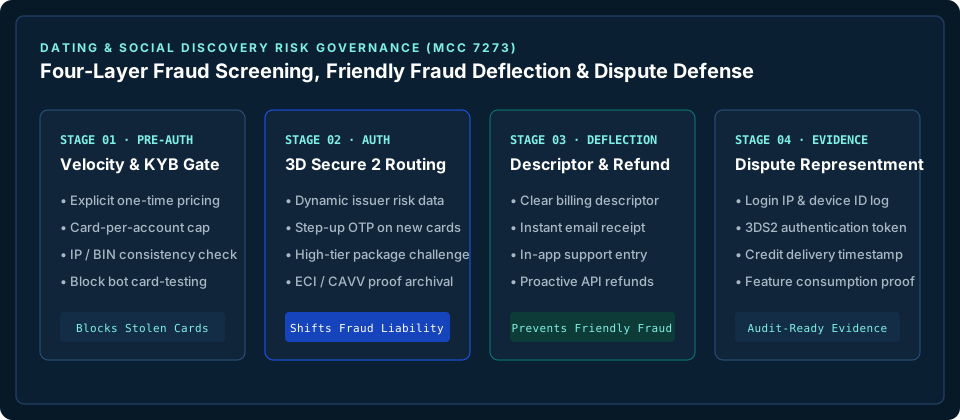
Four-Stage Fraud Screening, 3DS2 & Chargeback Defense Architecture
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Why must entitlement delivery wait for the server webhook instead of the return URL?
Users may close their browser before redirecting, or malicious actors may tamper with client URLs. Signed webhooks provide authoritative payment confirmation.
Can we sell 30-day VIP passes as one-time purchases?
Yes, provided the checkout clearly states it is a single one-time payment for a fixed 30-day entitlement without automatic renewal.
What should we show on the payment failure screen?
Display a clear failure reason, avoid automatic repeated retries on the same card, and provide an alternative payment attempt or support link.
Business assessment
Submit Your Dating Platform for Pre-Integration Review
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment