Security, Merchant Compliance & Data Governance Center
Review Cropay’s merchant KYB underwriting standards, prohibited business boundaries, payment data security principles, and legal compliance framework.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Sustainable payment processing requires transparent compliance boundaries. We separate verified operational rules from unverified marketing claims—ensuring merchant onboarding, data handling, and transaction flows align with regulatory and acquiring requirements.
Four Core Pillars of Security & Compliance
Merchant KYB & Business Underwriting
Verify corporate registration, ownership structure, business model, and historical risk prior to opening any acquiring channel.
Website & Product Inspection
Ensure merchant platforms display clear pricing, terms of service, privacy notices, refund policies, and customer support contacts.
Payment Data & API Security
Enforce HTTPS encryption, webhook signature verification, and strict separation of cardholder data according to integration mode.
Prohibited Business Enforcement
Strictly exclude illegal content, non-consensual adult material, unlicensed gambling, fraud, and deceptive billing practices.
Compliance Review Lifecycle
01 Pre-Onboarding Screening
Assess industry category, target jurisdictions, and prohibited business exclusions.
02 Document & Website Audit
Review corporate KYB documents alongside live website/app user flows and legal disclosures.
03 Technical & Data Boundary Check
Confirm checkout integration mode, webhook verification, and data protection practices.
04 Ongoing Post-Launch Monitoring
Monitor content changes, refund handling, and chargeback ratios throughout the merchant relationship.
Capabilities, Evidence & Compliance Boundaries
No Unverified License or Certification Claims
Specific regulatory licenses, PCI levels, or channel certifications are stated only where formally verified for the contracting entity.
Zero Tolerance for Prohibited Content
Any post-onboarding violation of acceptable use policies or undeclared domain switching will result in immediate suspension.
Not Legal Advice
Information on this website explains Cropay’s onboarding and operational framework and does not constitute formal legal advice.
Gateway sequence diagram
One-Time Checkout, 3DS2 & Signed Webhook Sequence Architecture
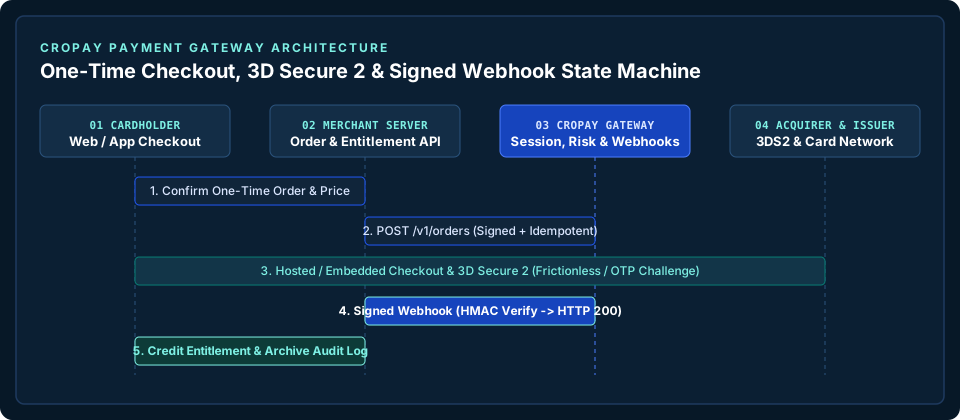
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Why does Cropay inspect our website and app before approving payment integration?
Acquiring banks and card networks require merchants to provide transparent pricing, clear terms, privacy disclosures, and accessible customer support before processing live transactions.
Should we send corporate ID documents or test card numbers through the public contact form?
No. The public contact form is for initial business inquiries only; KYB documents are collected through dedicated onboarding channels.
Where can we review Cropay’s Acceptable Use and Privacy Policies?
All 9 legal and compliance documents—including Privacy Policy, Acceptable Use Policy, and Merchant Compliance Guide—are available in the website footer.
Business assessment
Consult Our Compliance & Underwriting Team
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment