Streaming & Paid Digital Content Payment Guide: Pay-Per-View & Single Unlocks
Design compliant one-time payment flows for pay-per-view live events, VOD unlocks, and digital passes—ensuring clear entitlement rules and low disputes.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Author
Cropay Payment Architecture Editorial Team
Fact & Compliance Review
Cropay Business & Compliance Review Group
Last Fact Review
When users pay for a live broadcast ticket or a digital video unlock, disputes most often arise from unclear access windows, playback failures, or unexpected charges. Clear pre-purchase disclosures and immediate access verification keep conversion high and chargebacks low.
Key Elements of Paid Content Payment Architecture
Explicit Entitlement Disclosures
Specify whether the purchase grants permanent access, a 48-hour rental window, or a single live event ticket.
Instant Access Synchronization
Unlock playback immediately upon verified payment confirmation and provide a manual "refresh access" button.
Technical Playback Support
Provide fast customer support or automatic credit refunds if a live stream experiences technical outage.
Content & Copyright Compliance
Ensure all monetized media complies with copyright laws and platform acceptable use policies.
Pay-Per-View & Content Unlock Flow
01 Content Preview & Terms
Display content summary, device compatibility, access validity period, and one-time price.
02 One-Time Card Checkout
Process the card payment via Hosted or Embedded checkout with 3DS2 authentication.
03 Entitlement Token Issuance
Issue the viewing entitlement upon webhook confirmation and send an email receipt.
04 Playback Logging
Record stream start timestamps and session duration to verify service delivery.
Capabilities, Evidence & Compliance Boundaries
No Hidden Recurring Billing
Fixed-term passes (e.g., 7-day or 30-day access) must expire automatically without charging the card again.
Strict Content Legality
Platforms must hold legitimate rights to distribute paid content and strictly prohibit unlawful or non-consensual material.
Proactive Outage Handling
If a scheduled pay-per-view event is canceled, initiate batch refunds promptly to prevent mass disputes.
References & scope
References & Applicable Scope
Applicable Regions: Reviewed per merchant target markets and current regulatory policies
- Cropay Business Fact Baseline & Security Compliance Documentation (Verified on 2026-08-27)
Architecture blueprint
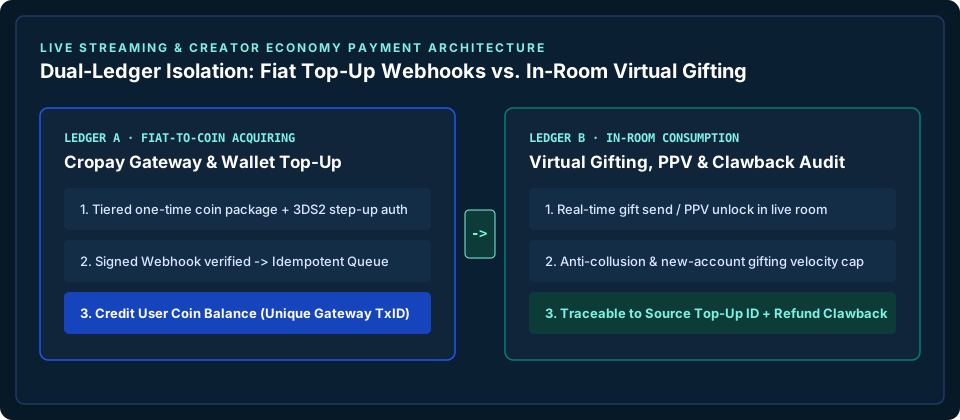
Dual-Ledger Top-Up & Virtual Gifting Payment Architecture
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Can we sell a 30-day streaming pass without recurring billing?
Yes. A one-time payment for a 30-day access pass that does not auto-renew is fully compatible with Cropay’s one-time transaction scope.
How do we reduce chargebacks on pay-per-view live events?
Test stream capacity in advance, state timezones clearly at checkout, send reminder receipts, and refund promptly if an event is canceled.
What proof of delivery works best for digital video purchases?
Authenticated payment records combined with server logs showing the user accessed and streamed the video after purchase.
Business assessment
Assess Your Paid Content & Streaming Payment Flow
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment