App & Web Payment Compliance Checklist for Digital Platforms
Pre-underwriting compliance checklist for dating, social, and live streaming apps—covering mandatory legal pages, pricing transparency, and support readiness.
Scope & readiness
Business & Capability Verification
Supported regions, card schemes, settlement cycles, and technical integration modes are verified item by item based on your merchant entity, business model, and acquiring approval.
Author
Cropay Payment Architecture Editorial Team
Fact & Compliance Review
Cropay Business & Compliance Review Group
Last Fact Review
Many merchant applications are delayed not by technical integration, but by missing website or app disclosures. Acquiring banks inspect your live product URLs to verify corporate identity, clear pricing, refund terms, privacy notices, and active content moderation.
Four Mandatory Compliance Checklists Before Applying
Corporate & Brand Consistency
Ensure the legal entity name, brand name, and contact details on your website match your KYB registration documents.
Checkout & Pricing Transparency
Display clear prices, currency symbols, item descriptions, and one-time payment disclosures before card entry.
Accessible Legal & Refund Policies
Provide public, non-login-gated links to your Terms of Use, Privacy Policy, Acceptable Use, and Refund Policy.
Customer Support & Complaint Channels
Publish a working customer service email or support ticket portal with clear response time expectations.
How to Prepare Your Platform for Underwriting
01 Self-Audit Against Checklist
Verify that all footer legal links, pricing pages, and support contacts are live and free of placeholder text.
02 Provide Test Account Credentials
Prepare a reviewer test account so underwriting teams can inspect the logged-in product and checkout flow.
03 Resolve Remediation Feedback
Update any unclear pricing copy, missing corporate disclosures, or content moderation gaps identified during review.
04 Lock Approved Domain Scope
Bind production gateway credentials strictly to the approved domain and app package names.
Capabilities, Evidence & Compliance Boundaries
No Undeclared Domain Switching
Routing traffic from unapproved domains or altered business models through an approved merchant account is strictly prohibited.
No Deceptive Marketing Copy
Websites must not use fake countdowns, misleading "free" claims, or hidden fees.
Compliance Is Continuous
Acquiring channels conduct periodic post-launch reviews of merchant websites and dispute ratios.
References & scope
References & Applicable Scope
Applicable Regions: Reviewed per merchant target markets and current regulatory policies
- Cropay Business Fact Baseline & Security Compliance Documentation (Verified on 2026-08-27)
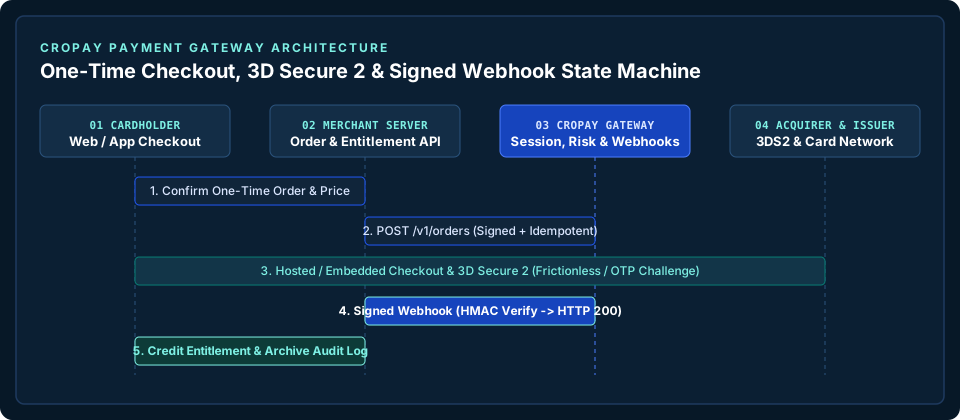
Gateway sequence diagram
One-Time Checkout, 3DS2 & Signed Webhook Sequence Architecture
Risk & compliance matrix
Platform Payment Risk, Prevention & Dispute Evidence Matrix
Structured matrix of common card dispute categories, pre-authorization prevention rules, and required representment evidence.
| Dispute / Risk Category | Typical Root Cause in Digital Platforms | Pre-Auth & Checkout Prevention | Required Audit & Representment Evidence |
|---|---|---|---|
| Unauthorized Card Fraud (Stolen / Testing) | Automated card testing bots or stolen credit cards used on new accounts | Per-user/card daily velocity caps, IP/BIN screening, mandatory 3DS2 step-up | 3DS2 authentication proof (ECI/CAVV), device fingerprint, and IP logs |
| Friendly Fraud (Unrecognized Descriptor) | Cardholder does not recognize legal corporate name on bank statement | Display exact billing descriptor at checkout and send instant email receipt | Order confirmation screenshot, email receipt log, and descriptor disclosure |
| Service / Entitlement Dispute | Delayed webhook credit, unclear one-time pass duration, or hidden support | Idempotent webhook + query fallback, explicit one-time terms, fast refund link | Timestamped wallet credit ledger, login session, and feature/coin usage logs |
Industry standards & regulatory references
External Technical Standards & Compliance Authorities
EMVCo 3-D Secure (3DS2) Specification
Global technical specification for EMV 3-D Secure (3DS2) frictionless and challenge authentication flows.
PCI Security Standards Council (PCI DSS)
Payment Card Industry Data Security Standard (PCI DSS) requirements for Hosted, Embedded, and API cardholder data protection.
Office of the Privacy Commissioner for Personal Data, Hong Kong (PCPD)
Official guidance on the Personal Data (Privacy) Ordinance (Cap. 486) and cross-border data compliance in Hong Kong.
FAQ
Frequently Asked Questions
Can our legal policies be visible only after a user logs in?
No. Acquiring banks and card networks require Terms of Service, Privacy Policy, Refund Policy, and Contact information to be publicly accessible.
Why do reviewers need a test login account for our app?
Because product catalog, coin packages, and checkout screens are typically inside the logged-in area and must be verified during underwriting.
What happens if we launch a new domain or app brand later?
Any new domain or app must be submitted for underwriting approval before processing live payments.
Business assessment
Request a Pre-Underwriting Website & App Compliance Check
Submit your corporate entity, website or app URL, target markets, billing items, transaction model, and preferred integration mode for a structured onboarding review.
Submit Onboarding Assessment